Identity Theft
How safe is my personal information?
Databreaches in Healthcare
What federal laws protect our medical information from improper exposure?
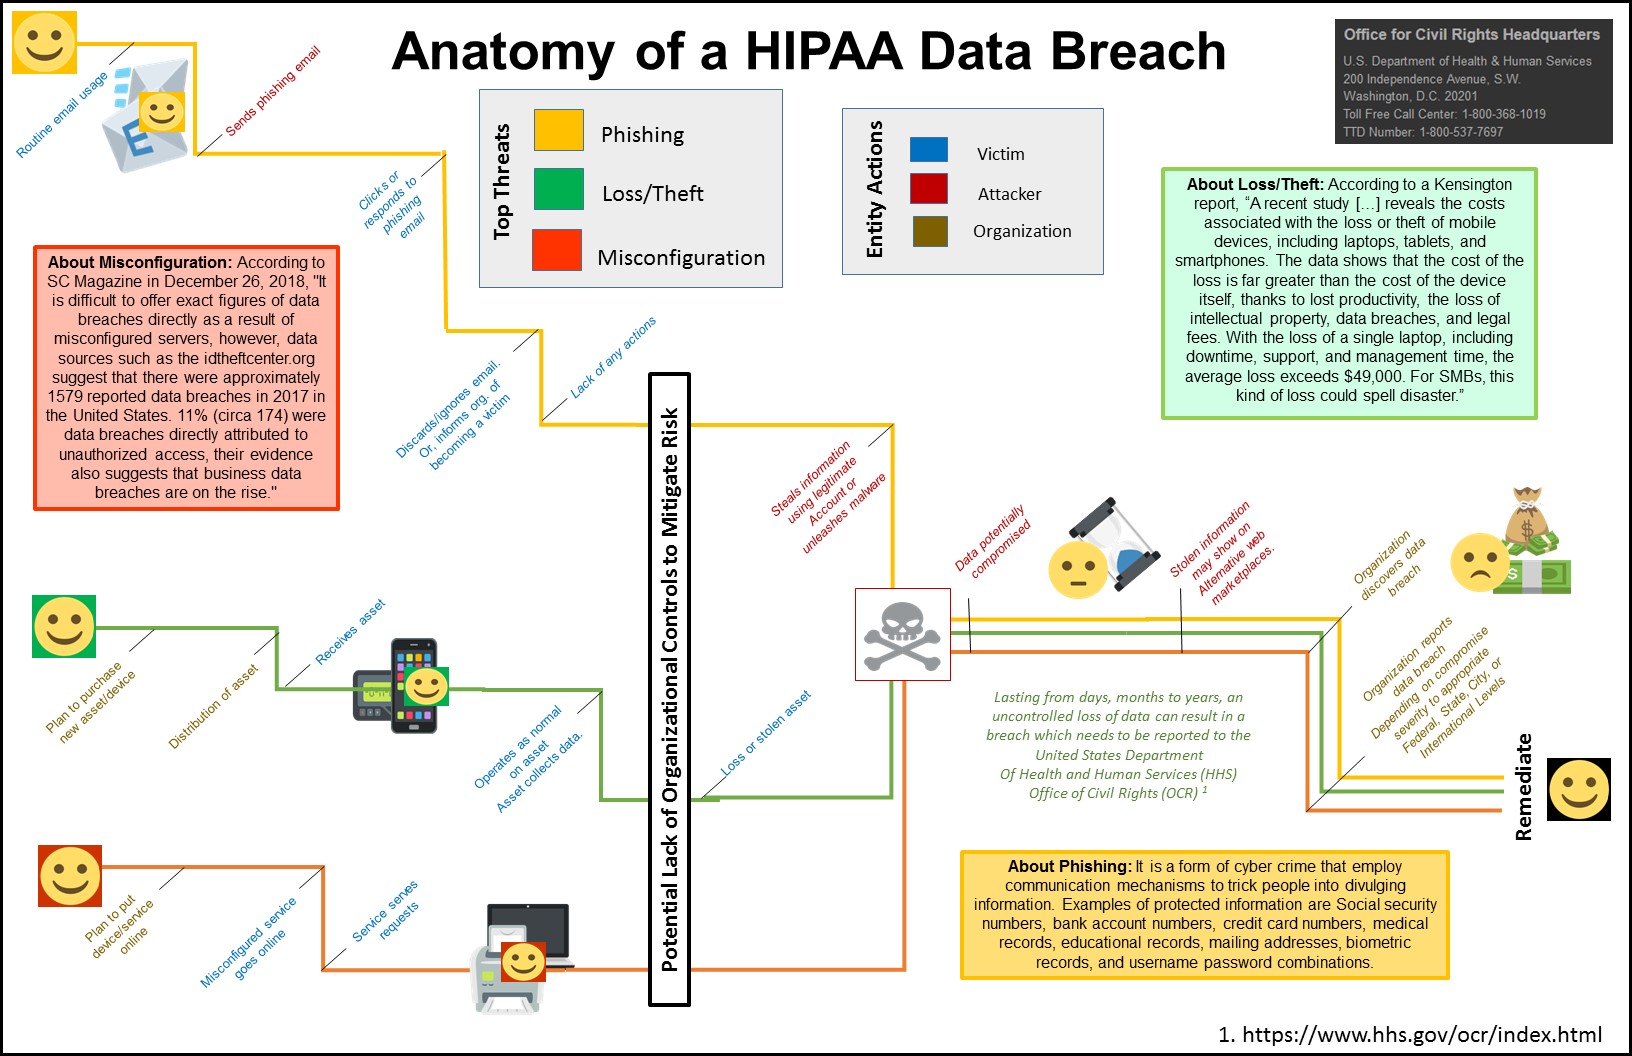
HIPAA/HITECH are two federal laws aimed at protecting the privacy and security of electronic health information. HITECH requires public notifications of breaches investigated by the U.S. Department of Health and Human Services' (HHS) Office for Civil Rights (OCR).
What is electronic Patient Health Information?
18 ePHI Identifiers
What are the Top Three breaches of 2019
investigated by OCR?
Top 2019 Breaches Reported to OCR as of May 2019.
What can happen when data is breached?
Databreaches can lead to identity theft
-
 Buy property in your name.
-
 Open accounts in your name.
-
 Not easy to fix.
-
 Can plague victim for years.
Who must follow HIPAA/HITECH?
-
Business Associate
An entity or person that performs activities or services on ePHI on behalf of a covered entity. -
Healthcare Provider
Conduct certain business electronically (e.g. doctors, clinics, hospitals, psychologists, chiropractors, nursing homes, pharmacies, and dentists). -
Health Plan
Health insurance companies, HMOs, company health plans, and government programs that pay for health care, e.g. Medicare/Medicaid.
How is the sensitive ePHI data being leaked?
Breaches Reported
by Covered Entities
5/1/2018 - 5/1/2019
OCR Data shows Covered Entities need different Risk Management
Healthcare Provider Breach Sources
Health Plan Breach Sources
Business Associate Breach Sources
5/1/2018 - 5/1/2019